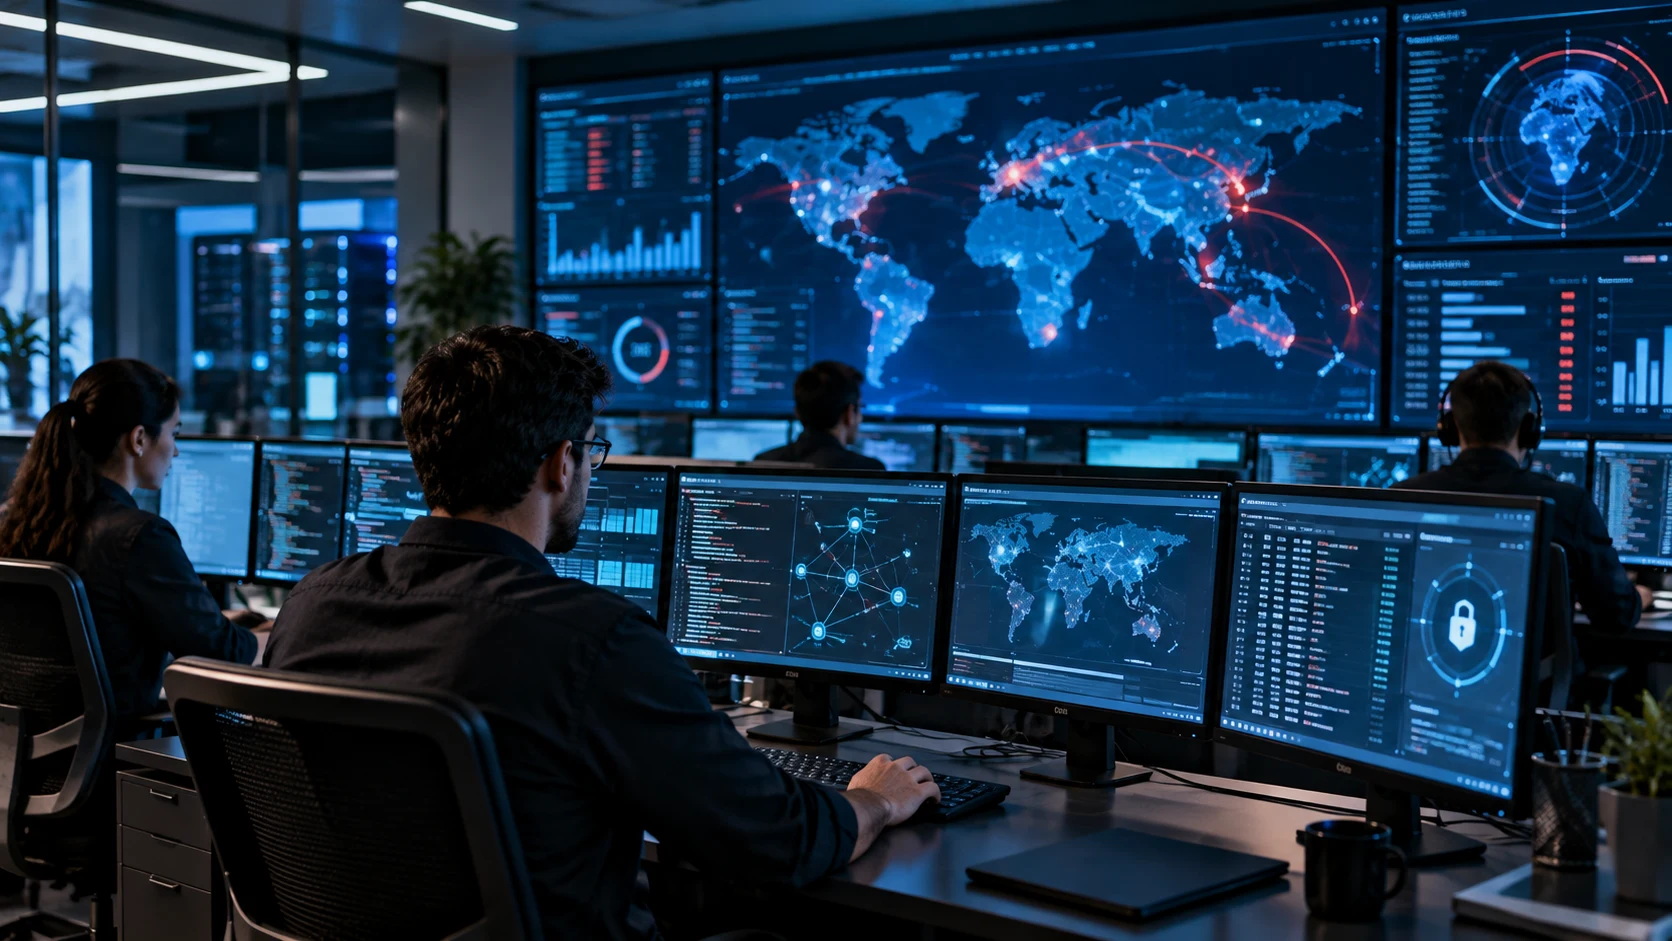
A Security Operations Center, commonly called a SOC, is one of the most important parts of modern cyber security. It acts as a central team responsible for monitoring systems, identifying suspicious activity, investigating threats, and responding to security incidents. Organizations use SOC teams to protect networks, devices, cloud platforms, applications, and sensitive information from cyber attacks.
A SOC combines skilled security professionals with monitoring tools, threat intelligence, automation, and documented response processes. Instead of waiting for an attack to cause serious damage, the team watches for warning signs and investigates unusual behavior as early as possible. This proactive approach helps reduce the potential impact of malware, ransomware, account compromise, and other threats.
Understanding what SOC means in cyber security is useful for business owners, IT professionals, students, and anyone considering a security career. This guide explains how a SOC works, what its analysts do, which tools it uses, how incidents are handled, and why security operations have become so important for modern organizations.
What Is a SOC in Cyber Security?
A Security Operations Center is a centralized function that continuously monitors an organization’s digital environment for possible security threats. The SOC may operate from a physical location, remotely, or through a managed security provider. Its main purpose is to detect suspicious activity quickly and coordinate an appropriate response before the problem becomes more serious.
SOC teams typically monitor network traffic, user activity, endpoints, cloud environments, servers, applications, and security logs. They look for unusual patterns that may indicate compromised accounts, malware infections, unauthorized access, or other threats. Information from multiple security systems is combined so analysts can understand what is happening across the organization.
A SOC is not simply a room filled with monitoring screens. It is a combination of people, processes, and technologies working together to improve security visibility. The team needs clear responsibilities, documented procedures, effective tools, and communication with other departments to respond efficiently when a potential cyber incident is discovered.
Why Is a SOC Important?
Organizations generate enormous amounts of security data every day from firewalls, computers, servers, applications, and cloud platforms. Without a dedicated monitoring function, important warning signs may be overlooked. A SOC helps organize this information and gives security professionals a central place to identify threats that could otherwise remain unnoticed.
Early detection can significantly reduce the damage caused by a cyber attack. If attackers gain access to a system and remain undetected, they may steal information, create additional accounts, spread malware, or move through the network. SOC analysts try to identify and contain suspicious behavior before attackers can expand their access.
A SOC also helps organizations build a more consistent approach to cyber security. Instead of responding differently every time something suspicious happens, analysts follow established processes for investigation, escalation, containment, and reporting. This structured response improves coordination and helps businesses learn from previous incidents.
What Does a SOC Team Do?
One of the main responsibilities of a SOC team is continuous security monitoring. Analysts review alerts from different systems and determine whether they represent real threats or harmless activity. Because security tools can generate many alerts, analysts must quickly prioritize the ones that could have the greatest impact.
SOC professionals also investigate suspicious events by reviewing logs, user activity, network connections, endpoint information, and other evidence. They try to understand what happened, which systems were affected, and whether an attacker still has access. This investigation helps determine how serious the incident is and what response is required.
Another important responsibility is documenting and improving security processes. After an incident, SOC teams may review what worked, what was missed, and how detection rules can be improved. These lessons can strengthen future monitoring and help the organization respond more effectively when similar security events occur again.
How Does a Security Operations Center Work?
A SOC begins by collecting security information from different systems across the organization. Logs may come from computers, servers, firewalls, applications, cloud services, identity systems, and network devices. Monitoring tools combine this data so analysts can search for suspicious patterns and receive alerts when certain security conditions are detected.
When an alert appears, a SOC analyst reviews the available information to determine whether it deserves further investigation. Some alerts may be false positives caused by normal business activity, while others may indicate genuine malicious behavior. Analysts compare the event with known attack patterns, threat intelligence, and activity from other systems.
If the event is confirmed as a security incident, the SOC follows its response procedures. Actions may include disabling a compromised account, isolating an infected endpoint, blocking a malicious address, or escalating the issue to another security team. The goal is to contain the threat quickly while preserving evidence for further investigation.
What Are the Main Roles in a SOC?
SOC teams often include several levels of analysts with different responsibilities and experience. Entry-level analysts may focus on reviewing alerts, checking basic evidence, and escalating suspicious activity. More experienced analysts usually investigate complex incidents, perform deeper analysis, and support containment or recovery activities.
Security engineers and detection specialists may also work with the SOC. They configure monitoring systems, improve alert rules, integrate new data sources, and maintain security tools. Their work helps ensure analysts receive useful information instead of being overwhelmed by unnecessary alerts from poorly configured systems.
SOC managers oversee the overall security operations function and coordinate people, processes, and reporting. They may track performance, manage incident response procedures, communicate with leadership, and plan improvements. Larger organizations may also include threat hunters, malware analysts, digital forensics specialists, and incident responders within or alongside the SOC.
What Tools Are Used in a SOC?
A Security Information and Event Management platform, often called a SIEM, is one of the most common SOC technologies. It collects and organizes security logs from multiple systems and helps analysts search for suspicious activity. SIEM tools can also create alerts based on unusual behavior, known threats, or predefined detection rules.
Endpoint detection and response tools are another important part of many SOC environments. These tools monitor computers, servers, and other endpoints for unusual behavior such as suspicious processes or malware activity. Analysts can use them to investigate affected systems and, in some cases, isolate a compromised device from the network.
SOC teams may also use firewalls, threat intelligence platforms, vulnerability scanners, intrusion detection systems, security automation tools, and network monitoring technologies. Learning how these systems work is valuable for anyone interested in security operations, especially those following a structured path to learn cyber security and build practical defensive skills.
What Is SOC Monitoring?
SOC monitoring is the continuous process of observing systems and security events for signs of suspicious activity. Rather than checking security manually only when a problem is reported, monitoring platforms collect information throughout the day. This provides greater visibility into what users, devices, applications, and networks are doing.
Monitoring may focus on failed login attempts, unusual account activity, unexpected network connections, malware detections, configuration changes, and other potentially risky behavior. A single event may not always be dangerous, so analysts often examine several pieces of information together before deciding whether an incident is occurring.
Effective monitoring depends on good visibility and useful detection rules. If important systems are not sending logs or alerts are poorly configured, the SOC may miss meaningful activity. Organizations therefore need to regularly review data sources, update detection logic, and ensure analysts receive information that supports accurate decisions.
How Does a SOC Handle Security Incidents?
Incident handling usually begins with detection and initial investigation. Once analysts identify suspicious activity, they gather evidence and determine whether the event is a genuine security problem. They may review login history, network connections, files, processes, alerts, and other information to understand the scope of the incident.
The next step is often containment. If an attacker has compromised an account or device, the organization needs to prevent the threat from spreading further. This may involve disabling credentials, blocking connections, isolating systems, or restricting access while investigators continue determining how the compromise occurred.
After containment, teams focus on removing the threat and restoring normal operations. They may delete malicious files, reset passwords, apply security updates, or restore systems from clean backups. The SOC then documents the incident and identifies improvements that could make future detection and response faster and more effective.
What Is the Difference Between SOC and NOC?
A SOC focuses primarily on security threats, suspicious activity, incidents, and protection of digital systems. Its analysts investigate potential attacks, malware, unauthorized access, and other cyber risks. Their main concern is whether something happening inside the environment creates a security problem that requires investigation or response.
A Network Operations Center, commonly called a NOC, focuses more on availability, performance, and reliability. NOC teams monitor networks, servers, bandwidth, outages, and technical problems that could affect business operations. Their goal is usually to keep technology functioning smoothly and resolve infrastructure issues quickly.
The two teams can work closely because operational problems and security incidents sometimes appear similar at first. A network slowdown may result from a technical failure, but it could also be caused by malicious activity. Sharing information between SOC and NOC teams can help organizations understand problems faster and respond appropriately.
What Is the Difference Between SOC and Incident Response?
The SOC handles continuous security monitoring and initial investigation across the organization’s environment. Its analysts watch for suspicious activity and determine whether an alert deserves escalation. Because this function operates continuously, the SOC often becomes the first security team to notice that something unusual is happening.
Incident response focuses more specifically on managing confirmed or serious security incidents. Incident responders may perform deeper investigations, containment, evidence collection, recovery, and communication during major events. They often become involved after the SOC determines that an alert represents a genuine threat requiring a coordinated response.
In some organizations, the same team performs both functions. Larger businesses may have dedicated SOC analysts and separate incident response specialists. Regardless of structure, the two functions need strong communication because rapid detection and effective response are closely connected during a cyber security incident.
What Skills Do SOC Analysts Need?
SOC analysts need a solid understanding of networking, operating systems, security fundamentals, and common cyber threats. They should be comfortable examining logs, understanding IP addresses and ports, investigating user activity, and identifying unusual system behavior. Knowledge of Windows and Linux environments can also be highly valuable.
Analytical thinking is equally important because alerts rarely provide every answer immediately. Analysts must compare information from several sources, identify patterns, and decide which events require additional attention. Strong problem-solving skills help them separate normal activity from behavior that may indicate a real attack.
Communication is another important SOC skill. Analysts frequently document investigations, create incident notes, escalate findings, and explain technical risks to other teams. Clear communication ensures that people responding to an incident understand what happened, which systems are affected, and what actions should be taken next.
What Are the Benefits of a SOC?
A major benefit of having a SOC is improved visibility across an organization’s digital environment. Security teams can monitor activity in one coordinated function instead of relying on isolated tools that nobody consistently reviews. Better visibility increases the likelihood that suspicious behavior will be noticed before it becomes a serious security incident.
A SOC can also improve response speed. When analysts are already monitoring alerts and following established procedures, they can investigate unusual events immediately rather than waiting for someone to report a problem. Faster detection and containment can reduce downtime, data exposure, and the overall impact of a successful cyber attack.
Another benefit is continuous improvement. SOC teams collect information about incidents, false positives, attacker techniques, and weaknesses in existing defenses. This information can be used to improve detection rules, strengthen security controls, and help the organization make better decisions about future cyber security investments.
What Challenges Do SOC Teams Face?
Alert overload is one of the biggest challenges in security operations. Monitoring tools can generate thousands of notifications, and many may not represent genuine threats. Analysts need effective filtering, prioritization, and automation so important incidents are not lost among large numbers of low-value alerts.
Another challenge is the constantly changing threat landscape. Attackers modify their techniques, exploit new vulnerabilities, and find ways to bypass existing defenses. SOC teams must continuously update their knowledge, monitoring rules, and security tools to keep up with new attack methods and emerging risks.
Staffing and skill development can also be difficult. Security monitoring requires trained professionals who can make accurate decisions under pressure. Organizations need to provide analysts with good processes, useful tools, manageable workloads, and ongoing training so the SOC can operate effectively over the long term.
Conclusion
A Security Operations Center is a central cyber security function that monitors systems, detects suspicious activity, investigates threats, and helps coordinate incident response. By combining people, processes, and technology, a SOC gives organizations greater visibility into what is happening across their digital environment.
SOC analysts use security logs, SIEM platforms, endpoint tools, threat intelligence, and other technologies to identify potential attacks. When a real incident occurs, they investigate the activity, help contain the threat, and support recovery. Their work can reduce the amount of time attackers remain undetected inside an organization.
As cyber threats continue to evolve, security operations remain an important part of protecting modern businesses. Organizations that build effective monitoring and response capabilities are better prepared to identify attacks early, limit their impact, and continuously improve their overall cyber security posture.
FAQs
What does SOC stand for in cyber security?
SOC stands for Security Operations Center. It is a centralized security function responsible for monitoring systems, investigating suspicious activity, detecting threats, and helping organizations respond to cyber security incidents.
What does a SOC analyst do?
A SOC analyst reviews security alerts, investigates suspicious activity, analyzes logs, identifies possible threats, and escalates confirmed incidents. Analysts also document findings and help improve monitoring and detection processes.
Is SOC part of cyber security?
Yes. A SOC is a major part of defensive cyber security because it focuses on continuous monitoring, threat detection, investigation, incident handling, and protecting an organization’s systems and information.
What tools do SOC analysts use?
SOC analysts commonly use SIEM platforms, endpoint detection tools, firewalls, vulnerability scanners, threat intelligence systems, network monitoring tools, and security automation technologies to detect and investigate suspicious activity.
Is SOC a good career for beginners?
SOC analyst roles can be a practical entry point into cyber security. Beginners usually benefit from learning networking, Windows, Linux, security fundamentals, log analysis, and common threat detection concepts before applying.