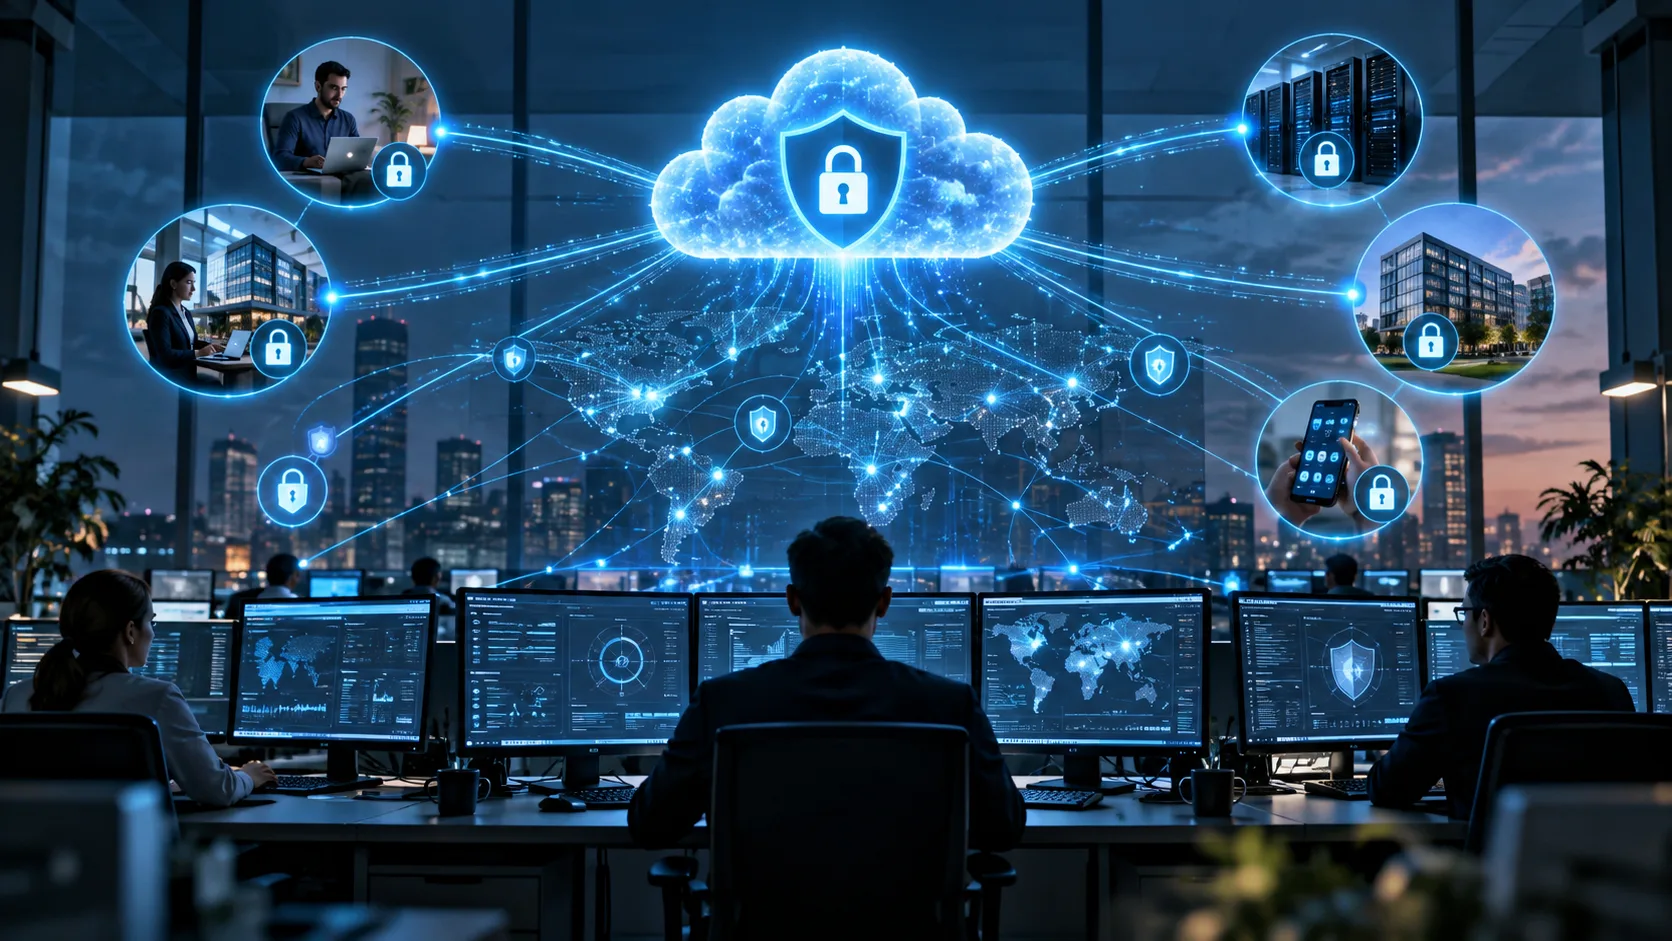
SASE, or Secure Access Service Edge, is a modern cybersecurity framework that combines networking and security functions into a unified cloud-based architecture. Instead of forcing users to connect through a central office or data center, SASE brings security controls closer to users, devices, applications, and cloud services. This makes it especially useful for remote work, cloud computing, and distributed business environments.
As organizations move away from traditional office networks, older security models can become difficult to manage. Employees may work from home, connect from public networks, use SaaS applications, and access company resources from multiple devices. SASE helps address these challenges by combining secure access, network optimization, identity-based controls, and cloud-delivered security into one integrated approach.
What Does SASE Mean in Cyber Security?
SASE stands for Secure Access Service Edge. The concept combines wide-area networking capabilities with security services that are delivered through the cloud. Instead of treating networking and cybersecurity as separate systems, SASE brings them together so users can connect securely to applications and data regardless of where they are located.
Traditional security architectures often rely on a central corporate network. Remote users may need to route traffic back through a company data center before accessing cloud applications, which can increase latency and create bottlenecks. SASE changes this model by applying security policies closer to the user through distributed cloud-based service points.
The goal is to provide secure, consistent access without depending entirely on physical network boundaries. Identity, device condition, application type, location, and security policies can all influence access decisions. This gives organizations a more flexible way to protect users while supporting cloud applications, remote work, branch offices, and mobile devices.
Why SASE Has Become Important
Business technology has changed significantly in recent years. Organizations now use cloud platforms, SaaS applications, remote employees, mobile devices, and distributed offices more than ever before. Traditional network security models were designed mainly around users working inside a company-controlled network, so they can become difficult to scale in modern environments.
SASE helps organizations secure traffic regardless of where users or applications are located. Instead of requiring every connection to pass through a central firewall at headquarters, security services can be delivered from the cloud. This can improve performance and provide more consistent protection for employees working from different cities, countries, or networks.
Another reason SASE is important is that businesses often use too many separate networking and security tools. Managing firewalls, VPNs, web gateways, access controls, and SD-WAN platforms separately can create complexity. SASE aims to simplify this environment by bringing several capabilities together under a more unified security and networking architecture.
How Does SASE Work?
SASE works by directing users and devices to nearby cloud-based service points where security policies are applied before access is granted. These service points evaluate traffic, identity, device information, and destination requirements. This allows security decisions to happen closer to users rather than requiring every request to return to a central office network.
The system can inspect traffic, block malicious websites, enforce access policies, protect cloud applications, and optimize network routes. Users may connect to SaaS applications, private business systems, or public internet services through the same secure architecture. Policies can remain consistent even when users change locations or connect from different devices.
SASE also uses identity as an important part of access control. Instead of trusting a device simply because it is connected to a company network, the system evaluates who the user is and what they are trying to access. This approach works closely with zero-trust principles and helps reduce the risk created by compromised accounts or devices.
Core Components of SASE
One of the main components of SASE is SD-WAN, or Software-Defined Wide Area Networking. SD-WAN helps organizations connect branch offices, cloud services, data centers, and remote locations using flexible network paths. It can automatically select better routes based on performance, availability, and business policies.
Another important component is Secure Web Gateway, often shortened to SWG. A secure web gateway monitors and controls user access to internet resources. It can block malicious websites, prevent risky downloads, enforce acceptable-use rules, and inspect web traffic for threats before they reach users or company systems.
SASE platforms may also include Cloud Access Security Broker, Firewall as a Service, and Zero Trust Network Access. Together, these technologies help protect cloud applications, filter network traffic, control access, and enforce security policies. The exact combination of features can vary depending on the SASE provider and the needs of the organization.
SASE and Zero Trust Network Access
Zero Trust Network Access, or ZTNA, is a key part of many SASE architectures. The zero-trust model assumes that users, devices, and connections should not automatically be trusted simply because they are inside a corporate network. Every access request should be verified according to identity, device condition, policy, and context.
ZTNA provides access to specific applications rather than giving users broad access to an entire internal network. This reduces the possibility of attackers moving freely between systems if an account becomes compromised. It also helps organizations apply different rules to employees, contractors, partners, and third-party users.
SASE combines ZTNA with networking and other cloud security capabilities. This creates a more complete architecture where identity-based access controls, web security, cloud protection, and traffic management work together. The result is a system designed for users who may never physically connect to a traditional company office.
SASE vs. Traditional VPN
Traditional VPNs create encrypted connections between remote users and company networks. They are useful for protecting traffic over untrusted networks, but they often provide broad network access once a user successfully connects. This can create security concerns when users only need access to one application but receive visibility into additional internal resources.
VPN architecture can also create performance problems when large numbers of remote employees route traffic through central infrastructure. A user may connect from one region to a corporate data center in another region before accessing a cloud application located somewhere else. This indirect path can increase latency and reduce application performance.
SASE uses distributed cloud service points and identity-based access to provide more direct and controlled connections. Rather than replacing every VPN immediately, organizations may gradually use ZTNA and SASE for specific users or applications. The best approach depends on existing infrastructure, security requirements, and the applications employees need to access.
SASE and Cloud Security
Cloud applications are now central to everyday business operations. Employees may use platforms for email, file storage, customer management, communication, accounting, and collaboration without connecting to a traditional data center. SASE provides a way to apply security policies consistently across these cloud-based services.
Cloud Access Security Broker capabilities can help organizations understand which cloud applications employees are using. Security teams can identify unauthorized services, enforce data protection policies, and control access to sensitive information. This is particularly useful when employees use multiple SaaS platforms across different departments.
Data protection also depends on technologies such as encryption, access controls, and secure authentication. SASE can work alongside these methods to protect data as users interact with cloud applications. Readers interested in another fundamental security concept can review this guide to hashing in cyber security to understand how data integrity can also be verified.
Benefits of SASE for Businesses
One major benefit of SASE is simplified security management. Instead of maintaining several independent networking and security tools, organizations can manage many policies through a more unified platform. This can reduce administrative complexity and help security teams apply consistent rules across offices, remote users, cloud environments, and mobile devices.
Performance can also improve because traffic does not always need to travel back through a central company network. Users can connect to nearby SASE service points and then reach their intended applications. This can reduce unnecessary routing and improve the experience of employees using cloud services from different geographic locations.
SASE can also improve scalability. When a company opens a new branch, hires remote employees, or adopts new cloud applications, security controls can often be extended without deploying large amounts of physical hardware. Cloud-delivered security makes it easier to support business growth and distributed working environments.
Security Risks SASE Can Help Reduce
SASE can help reduce risks associated with unauthorized access. Identity-based policies allow organizations to limit users to the resources they actually need. If an employee account is compromised, restricted access can make it more difficult for an attacker to move laterally through internal systems.
Web security features can also help block phishing websites, malware downloads, and suspicious internet activity. Secure web gateways and cloud firewalls inspect traffic and apply security policies before potentially harmful content reaches users. This creates an additional layer of protection beyond endpoint antivirus or user awareness training.
SASE also improves visibility across distributed environments. Security teams can monitor users, applications, access attempts, and traffic from a centralized platform. Better visibility makes unusual behavior easier to detect and can support faster incident investigation when suspicious activity appears across remote users or cloud services.
Challenges of Implementing SASE
Moving to SASE is not always simple. Organizations may already have firewalls, VPNs, SD-WAN systems, cloud security products, and identity platforms that need to be integrated or replaced. A rushed migration can create confusion, duplicate controls, or gaps between old and new security systems.
Vendor selection is another challenge because not every platform provides the same capabilities. Some providers may be stronger in networking, while others focus more heavily on security. Organizations should evaluate performance, geographic coverage, integration options, identity support, monitoring, data protection, and management features before choosing a solution.
Businesses also need people with the right skills. SASE combines networking, cloud computing, cybersecurity, and identity management, which means teams may need to work across traditional departmental boundaries. Training and clear responsibility are important so employees understand how policies are designed, monitored, tested, and updated over time.
How to Implement SASE Successfully
The first step is understanding the existing environment. Organizations should identify users, branch offices, cloud applications, private systems, network connections, VPN usage, security tools, and access requirements. This assessment helps teams understand which problems SASE should solve rather than implementing new technology without a clear business goal.
Next, companies should prioritize use cases. Remote access may be the first area to modernize, while another organization may focus on branch connectivity or cloud security. A phased approach allows teams to test performance and security controls before moving the entire organization onto a new architecture.
Finally, organizations should continuously monitor the environment after deployment. Security policies, application usage, user behavior, and business requirements change over time. Regular reviews help ensure that access controls remain appropriate and that the SASE platform continues supporting both performance and security goals.
SASE Best Practices
Use identity as the foundation of access decisions. Strong authentication, multi-factor authentication, device verification, and least-privilege access help ensure that users receive only the permissions they genuinely need. This is especially important when employees, contractors, and partners access systems from outside traditional company networks.
Organizations should also segment access wherever possible. A user who needs one business application should not automatically receive access to unrelated internal resources. Application-level access limits potential attack paths and helps reduce the damage that can occur when credentials or devices become compromised.
Monitoring should remain continuous rather than being treated as a one-time configuration task. Review security alerts, access patterns, application usage, and network performance regularly. These insights can help security teams improve policies, detect suspicious behavior, and identify performance problems before they significantly affect employees.
Conclusion
SASE in cyber security stands for Secure Access Service Edge. It combines networking and security capabilities through a cloud-delivered architecture designed for modern distributed organizations. Technologies such as SD-WAN, ZTNA, secure web gateways, cloud security controls, and cloud firewalls can work together under a more unified framework.
The main advantage of SASE is that security can follow users rather than depending entirely on the physical company network. Employees can work from offices, homes, hotels, or other locations while still being subject to consistent identity and security policies. This flexibility makes SASE particularly useful for cloud-based businesses and remote work environments.
SASE is not simply one product that solves every security problem. Successful implementation requires careful planning, identity management, policy design, monitoring, and integration with existing systems. When implemented correctly, it can simplify network security while improving visibility, access control, performance, and protection across distributed environments.
FAQs
What does SASE stand for in cyber security?
SASE stands for Secure Access Service Edge. It combines networking and cloud-delivered security services to provide secure access to applications, websites, and business resources from different locations and devices.
Is SASE the same as zero trust?
No. Zero trust is a broader security principle focused on continuous verification and least-privilege access. SASE can include Zero Trust Network Access as one of several networking and security capabilities.
Does SASE replace a VPN?
SASE can reduce dependence on traditional VPNs by using identity-based ZTNA for application access. However, some organizations may continue using VPNs for particular systems or during a gradual migration.
What are the main components of SASE?
Common SASE components include SD-WAN, Zero Trust Network Access, Secure Web Gateway, Cloud Access Security Broker, and Firewall as a Service. Features vary depending on the provider and organization.
Why do businesses use SASE?
Businesses use SASE to secure remote users, simplify networking and security management, protect cloud applications, improve access control, and provide more consistent security across offices, devices, and distributed work environments.